Wiz Discloses Gheist Campaign Implanting Malicious GitHub Actions Workflows
Wiz revealed the Gheist campaign, where attackers abused stolen GitHub tokens across over 850 accounts to implant over 13,500 malicious branches, targeting secrets via Actions workflows and self-hosted runners across roughly 12 firms.
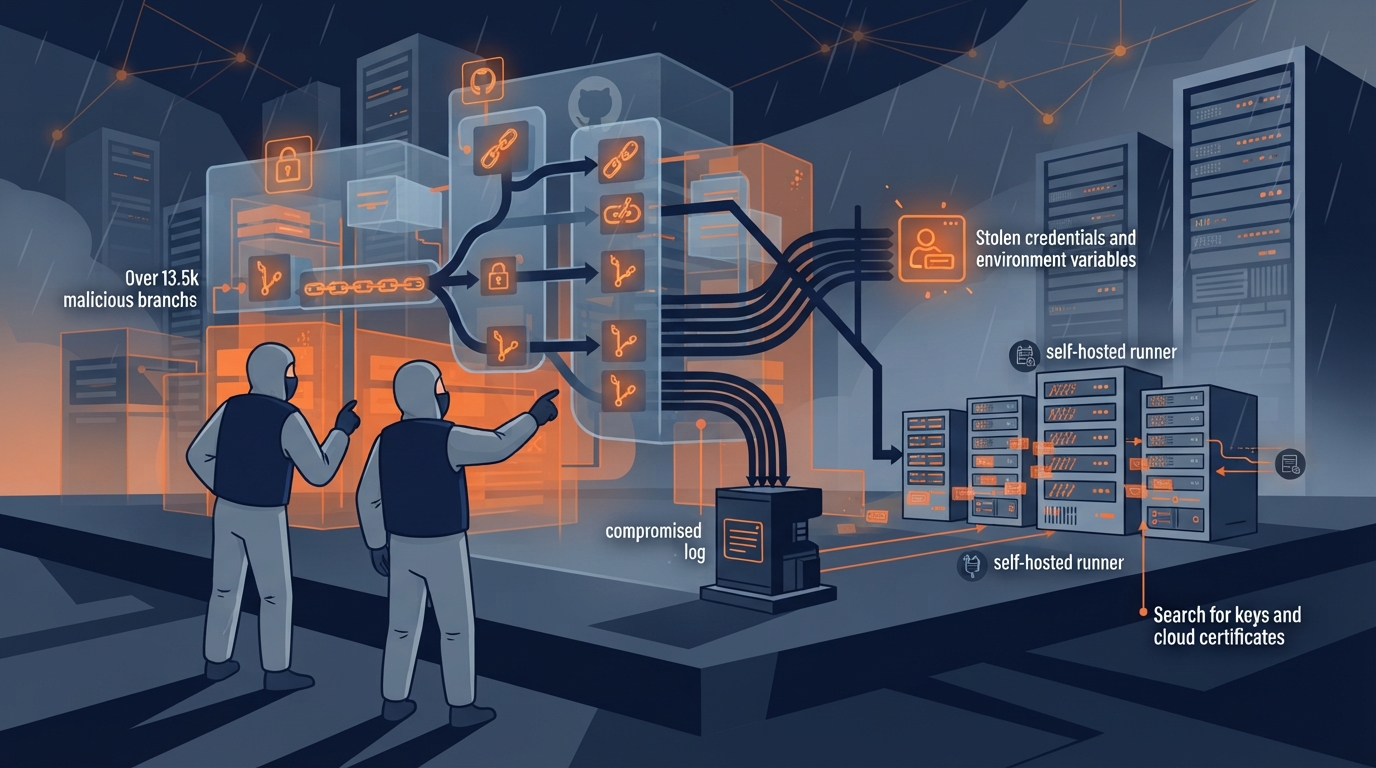
Wiz revealed the Gheist campaign compromised over 850 GitHub accounts and created over 13,500 malicious branches from mid-September to late October. While public repositories require approval for suspicious workflows, private and enterprise instances saw successful executions. Attackers encoded secrets into logs to bypass masking before deletion, and searched self-hosted runners for cloud credentials.
Key takeaways
- Attackers abused stolen GitHub tokens across over 850 accounts to implant over 13,500 branches, affecting an estimated 12 firms.
- Malicious workflows encoded secrets into logs to bypass masking and targeted self-hosted runners to extract cloud credentials.
Source:iThome Read the original ↗
Prepared, checked and automatically published by AI; not individually reviewed by a human. Translation checked by AI.