EU ENISA Issues SBOM Technical Advisory Outlining Lifecycle and Security Guidelines
The European Union Agency for Cybersecurity (ENISA) released an SBOM technical advisory on October 22, detailing a six-stage lifecycle to address Cyber Resilience Act obligations and mitigate supply chain tampering risks.
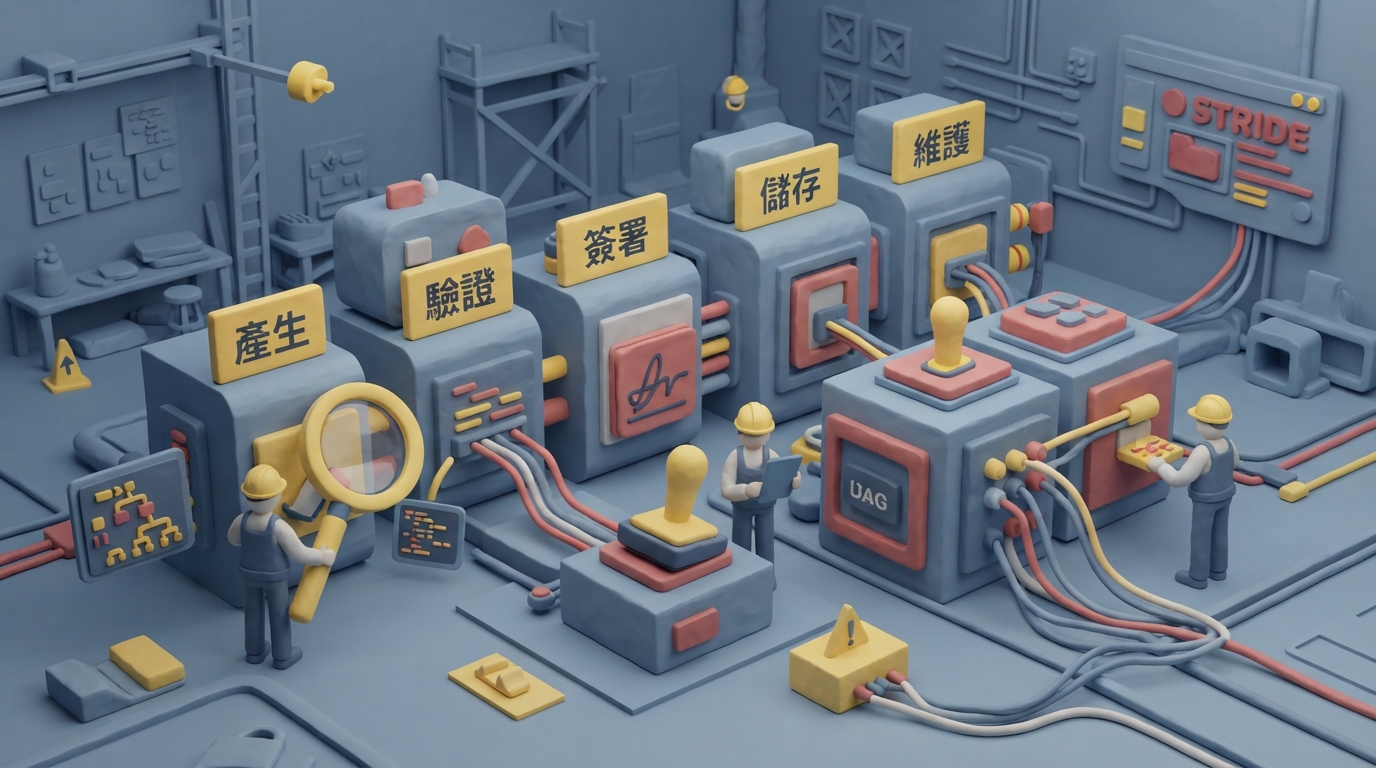
ENISA officially released the ENISA Technical Advisory for Software Bill of Materials on October 22, detailing a six-stage lifecycle covering generation, validation, signing, storage, consumption, and maintenance within CI/CD pipelines. Developed to assist organizations with Cyber Resilience Act requirements, ENISA stressed that the non-binding technical advisory does not alter legal obligations or provide formal legal interpretations.
Key takeaways
- ENISA outlined a six-stage SBOM lifecycle and categorized open-source tools such as Syft and Cosign across CycloneDX and SPDX formats to support implementation.
- Using the STRIDE threat model, the advisory highlighted risks like tampering and spoofing, recommending digital signatures, authentication, and access controls to maintain integrity.
Source:iThome Read the original ↗
Prepared, checked and automatically published by AI; not individually reviewed by a human. Translation checked by AI.