LiteLLM Details Supply Chain Attack Behind Malicious v1.107.0 Release
Frontier AI models · AI assistants · Enterprise AI
LiteLLM published a post-incident analysis explaining how an unrevoked admin key exposed months earlier led to a supply chain breach. The attacker extracted unscoped GitHub CLI OAuth tokens, modified release pipelines, bypassed branch protection, and published compromised v1.107.0 packages to PyPI and container registries before artifacts were removed.
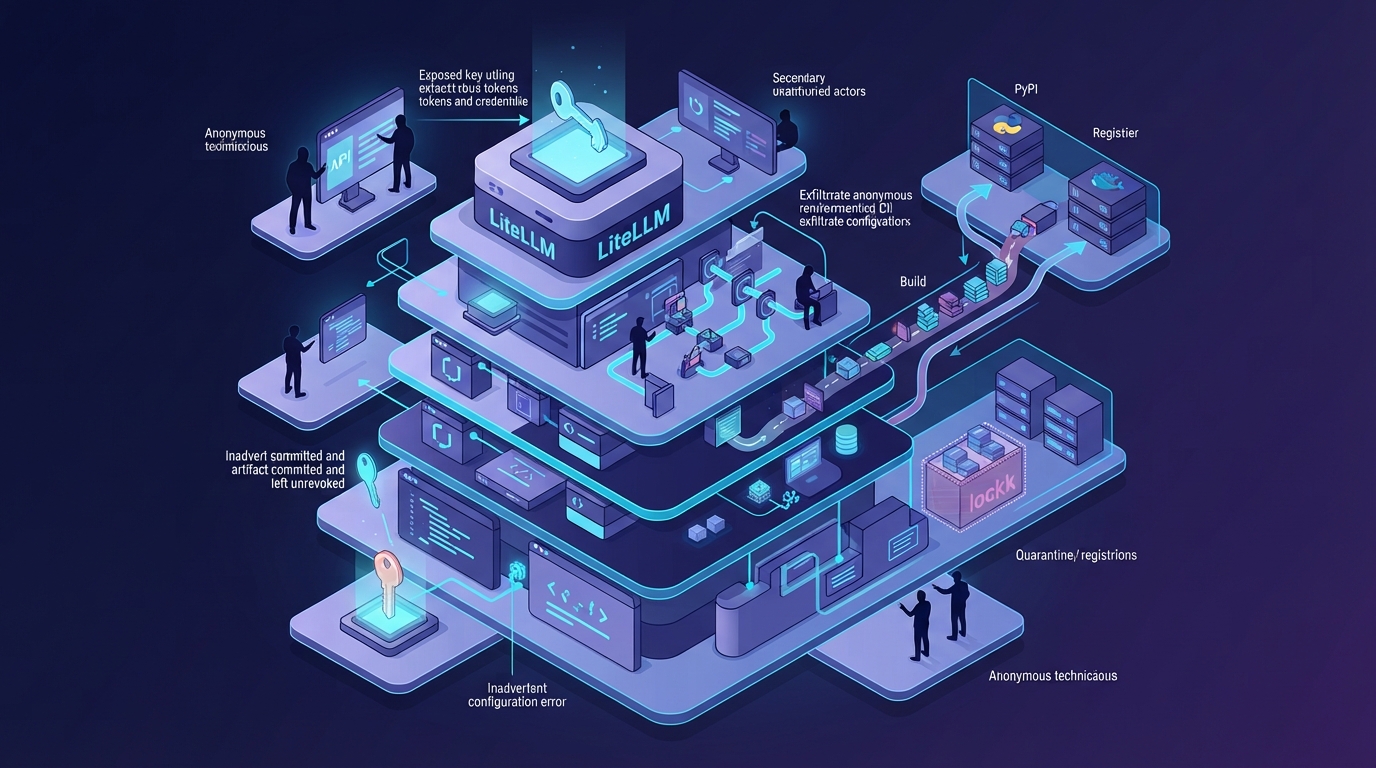
On October 23, 2026, LiteLLM released an incident root cause analysis describing the attack chain that led to the compromised litellm==1.107.0 release published on October 21. According to the team, the intrusion stemmed from a configuration file inadvertently committed to a public repository on May 27 containing an administrative key to an internal LiteLLM Agent Platform deployment. Although the file was deleted hours later, the key was not revoked. On October 10, an attacker used the key to query the platform API and extract a GitHub CLI OAuth token belonging to an organization owner. The token lacked fine-grained scoping and was not subject to GitHub's super-user two-factor reauthentication flows. With owner privileges, the attacker ran CI workflows on throwaway branches across internal repositories to exfiltrate additional maintainer credentials and pipeline secrets. On October 21, the attacker modified the private release workflow to point build sources to a lookalike fork (Berri-AI/litellm), bypassed branch protection using owner permissions, and leveraged multiple stolen maintainer tokens to satisfy relaxed release approval checks. Malicious wheels were subsequently pushed to PyPI and Docker registries before LiteLLM detected the anomaly, quarantined packages, locked registries, and revoked internal tokens.
Key takeaways
- An administrative key mistakenly committed to a public repository in May 2026 remained unrevoked for over four months, allowing an attacker to access the LiteLLM Agent Platform API on October 10.
- The attacker extracted an unscoped GitHub CLI OAuth token belonging to an organization owner, enabling branch protection overrides and secret exfiltration across internal CI workflows.
- By altering private release workflows and using multiple stolen tokens, the attacker satisfied relaxed multi-person release approvals and published malicious v1.107.0 packages to PyPI and container registries.
- LiteLLM identified the incident on October 21, removed and quarantined compromised artifacts within hours, cleared organization memberships, and initiated full credential revocation.
Source:docs.litellm.ai Read the original ↗
Prepared, checked and automatically published by AI; not individually reviewed by a human.