Researcher Detects First Successful PHP2Shell Exploits in Honeypot
Perplexity researcher Adel Karimi detected attackers exploiting PHP2Shell vulnerabilities (CVE-2026-109618, CVE-2026-109619) in a honeypot running PHP 8.4.26 with Apache mod_php, marking the first observed arbitrary code execution.
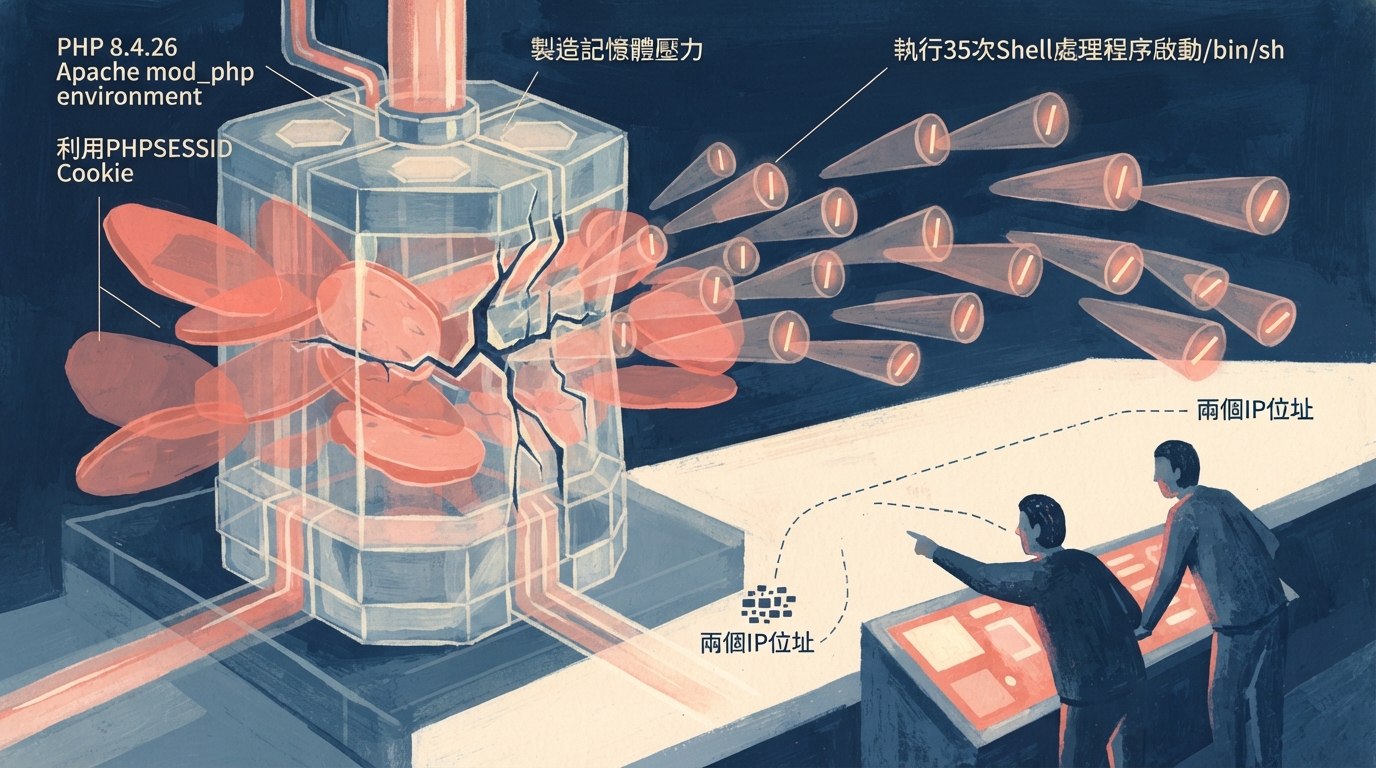
Perplexity researcher Adel Karimi detected PHP2Shell exploitation in a honeypot. Target systems ran PHP 8.4.26 with Apache mod_php, where attackers triggered 35 shell process executions to launch /bin/sh across four stages involving memory pressure and PHPSESSID manipulation. Although security teams originally noted exploitation would be difficult, this confirms arbitrary code execution has been achieved.
Key takeaways
- The honeypot logged 35 shell process executions across four attack stages, including creating memory pressure and obtaining memory info via oversized PHPSESSID cookies.
- Attacks originated from two IP addresses sharing templates and hash traits without shared control mechanisms; researcher noted attribution remains unconfirmed.
Source:iThome Read the original ↗
Prepared, checked and automatically published by AI; not individually reviewed by a human. Translation checked by AI.