Scaling AI Agent Governance with Okta Cross App Access and Amazon Bedrock AgentCore
AI assistants · Enterprise AI
AWS detailed how to scale enterprise AI agent governance by introducing Amazon Bedrock AgentCore Gateway and Cedar policy evaluation. Moving beyond point-to-point agent connections, the pattern places token exchange and Cedar authorization at a central gateway. This setup isolates agent credentials, applies unified default-deny policies before tool invocation, and supports external agents hosted on Amazon EKS while streaming audit spans into CloudWatch.
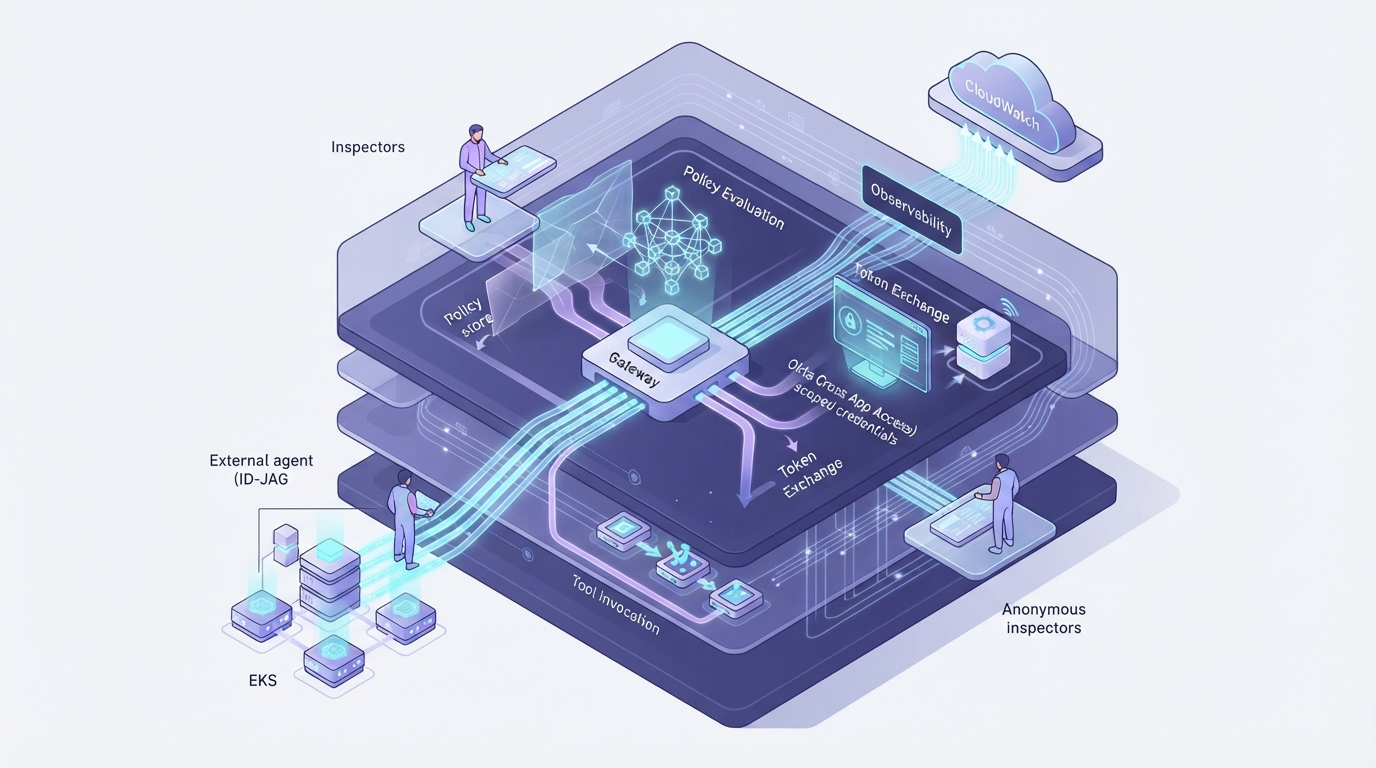
AWS shared an architecture pattern to govern enterprise AI agents at scale using Okta Cross App Access (XAA) and Amazon Bedrock AgentCore capabilities. In single-agent setups, task agents often connect directly to Model Context Protocol (MCP) servers and manage their own token exchanges, which becomes unmanageable across hundreds of agents and thousands of tools. Under the scaled architecture, Amazon Bedrock AgentCore Gateway acts as a centralized entry point. Agents forward the Identity Assertion JWT Authorization Grant (ID-JAG) directly to the gateway, removing secret-handling and token-exchange permissions from individual agent execution roles. Within this architecture, Policy in AgentCore evaluates default-deny Cedar policies to verify agent identity and delegated scopes before any target tool runs. If authorized, the gateway orchestrates token exchange via AgentCore Identity against Okta's authorization server to invoke downstream MCP targets. AWS also demonstrated hosting a secondary reporting agent on Amazon Elastic Kubernetes Service (Amazon EKS) to show that the gateway architecture functions consistently regardless of where the runtime executes. System decisions across runtime, gateway, policy, and Okta are tracked using OpenTelemetry spans and routed through AgentCore Observability to Amazon CloudWatch for unified auditing.
Key takeaways
- Amazon Bedrock AgentCore Gateway serves as a unified entry point, removing token-exchange and secret-reading privileges from individual agent roles.
- Policy in AgentCore evaluates default-deny Cedar policies at the gateway layer before tool execution, replacing duplicated code-level checks across MCP servers.
- The setup supports agents running outside the native runtime, demonstrated via a reporting agent hosted on Amazon EKS with pod-level IAM controls.
- AgentCore Observability and Amazon CloudWatch collect OpenTelemetry spans across each hop, unifying agent authorization decisions and Okta system logs.
Source:AWS Machine Learning Read the original ↗
Prepared, checked and automatically published by AI; not individually reviewed by a human.